"TotalRecall Reloaded" tool finds a side entrance to Windows 11's Recall database
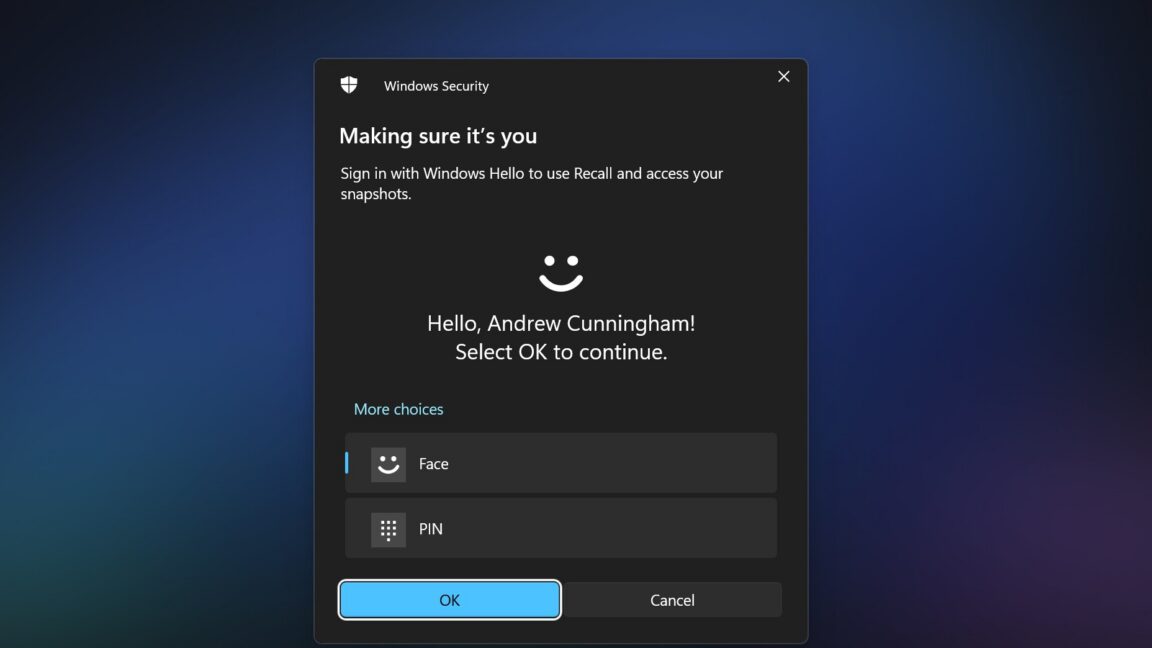
Two years ago, Microsoft launched its first wave of “Copilot+” Windows PCs with a handful of exclusive features that could take advantage of the neural processing unit (NPU) hardware being built into newer laptop processors. These NPUs could enable some AI and machine learning features that could be run locally rather than in someone’s cloud, theoretically enhancing security and privacy. One of the first Copilot+ features was Recall, a feature that promised to track all your PC usage via screenshot to help you remember your past activity. But as originally implemented, Recall was neither private nor secure ; the feature stored its screenshots plus a giant database of all user activity in totally unencrypted files on the user’s disk, making it trivial for anyone with remote or local access to grab days, weeks, or even months of sensitive data, depending on the age of the user’s Recall database. After journalists and security researchers discovered and detailed these flaws, Microsoft delayed the Recall rollout by almost a year , substantially overhauling its security . All locally stored data would now be encrypted and viewable only with Windows Hello authentication; the feature now did a better job detecting and excluding sensitive information, including financial information, from its database; and Recall would be turned off by default, rather than enabled on every PC that supported it. Read full article Comments
“The vault is solid. The delivery truck is not.”
The reconstituted Recall was a big improvement , but having a feature that records the vast majority of your PC usage is still a security and privacy risk. Security researcher Alexander Hagenah was the author of the original “TotalRecall” tool that made it trivially simple to grab the Recall information on any Windows PC, and an updated “TotalRecall Reloaded” version exposes what Hagenah believes are additional vulnerabilities.
The problem, as detailed by Hagenah on the TotalRecall GitHub page , isn’t with the security around the Recall database, which he calls “rock solid.” The problem is that, once the user has authenticated, the system passes Recall data to another system process called AIXHost.exe , and that process doesn’t benefit from the same security protections as the rest of Recall.